
We renewed teh certificate on our internal API yesterday. On my desktop browser everything looks fine. But Python requests now fails with:
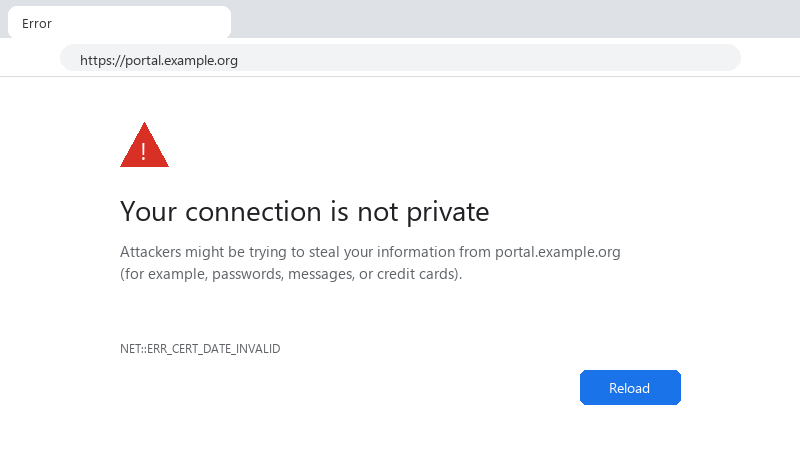
Your connection is not private
Attackers might be trying to steal your information from portal.example.org
(for example, passwords, messages, or credit cards).
NET::ERR_CERT_DATE_INVALID
the certificate isnt expired, the name matches... nothing else changed... why would only some clients complain??
Ive checked the dates, the hostname and the isuser. Everything looks correct when i click the padlock in my browser. Im clearly missing something, but i dont know what tool shows what the client actually receives.


