CERT RENEWED, BROWSER STILL SCREAMS NET::ERR_CERT_AUTHORITY_INVALID. HUH?? lol

Solvedcertificatelets-encryptssl6 replies · 199 views · started
Accepted solution by Zane — hmmm with Certbot, run sudo certbot renew dry run to see whether renewal would work right now. Check teh timer with systemctl list timers…
  1. long time lurker first post lol well, this is embarrassing. our staging server is serving a certificate error and i only found out when i tried to log in myself.
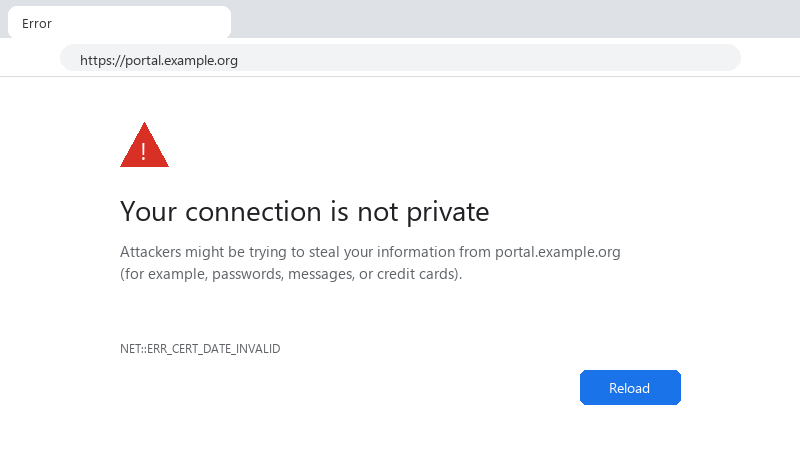
    Your connection is not private

    Your connection is not private
    Attackers might be trying to steal your information from portal.example.org
    (for example, passwords, messages, or credit cards).
    NET::ERR_CERT_DATE_INVALID
    

    NET::ERR_CERT_AUTHORITY_INVALID. Im using the hosts free SSL toggle. I tried running a renewal manually and it either says nothing needs renewing or fails with a challenge error I dont understand lol Which one is lying, teh browser or teh tool? Id really like to know which part of teh chain failed so I can monitor it.

    6
  2. wait did anything change with DNS, firewall rules or redirects recently? ?

    5 0 helpful
  3. long time lurker first post lol told my boss it would take 10 minuets. its been 3 hours any ideas??

    1 0 helpful
  4. oof renewal can succeed while the browser still sees the old cert, because the web server loaded teh certificate at startup and never reloaded. Add a deploy hook: certbot renew --deploy-hook "systemctl reload nginx" (or apache2). conatiners need the same: reload or restart teh proxy after renewal. good luck man!

    0 8 helpful
  5. Accepted solution

    hmmm with Certbot, run sudo certbot renew --dry-run to see whether renewal would work right now. Check teh timer with systemctl list-timers | grep certbot 👍 common failures: port 80 blocked by a firewall, a redirect rule that breaks /.well-known/acme-challenge/, or DNS now pointing somewhere else.

    2 5 helpful
  6. @packetlab reopened port 80 just for teh ACME challenge path and renewal worked... added expiry monitoring too, lesson learned. cant believe it was that simple lol

    thumbsup

    2 0 helpful

Reply to this topic

Sign in or create an account to reply.