dnssec validation failure - my site is gone?? ugh

dns-recordsdnssecdomain-management3 replies · 3 views · started
  1. so i was messing around with some dnssec records on my production domain trying to haredn teh security a bit, and suddenly my site just... vanished from the web. it is literally returning an NXDOMAIN or a validation error depending on which resolver i check. i checked the records and everything looks correct on my end, but it seems like the chain of trust is totally broken.
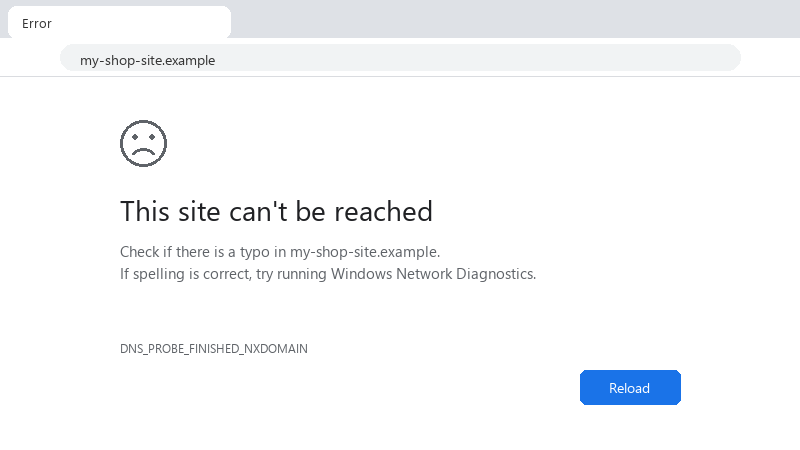
    dns error

    i have already verified the RRSIG and DNSKEY records against what the registrar is showing, and i even tried flushing the cache on my local machine but that obviously won't fix a propagation/validation issue at the resolver level. honestly i am panicking a bit cuz this is a live project and i dont have any way to reach the backend right now. it feels like i just nuked my own house while trying to install a deadbolt.

    Is there any chance i messed up the DS record at the registrar level?? Im worried about teh propagation time for these fixes. has anyone else dealt with a situation where teh records look perfect but the validation just refuses to cooperate?? id really appreciate some eyes on this before i start pulling my hair out lol.

    0
  2. double check your DS record at the registrar. if the key tag or digest doesnt match the current DNSKEY exactly, the chain breaks and resolvers will drop it. also check if your zone's expiration dates on the RRSIGs are actually valid... sometimes it's just a simple clock drift on the nameserver.

    0 0 helpful
  3. i hear what @clarar886 is saying about the DS records, but honestly i'd be careful about jumping straight to clock drift unless u have a specific reason to suspect the nameserver time. in a setup like mine, if the records look perfect but it's still throwing NXDOMAIN, i usually suspect a mismatch between the zone's signature period and the actual keys being served.

    imo, if u've already verified the keys against the registrar, the issue might be that the RRSIGs haven't been fully re-signed for the new key yet. even if the DS record is 'right' now, some resolvers are still holding onto the old signatures for a bit. it's like trying to change the locks while people are still trying to use the old keys... total headache.

    instead of just checking the clock, i'd try to see if u can get a tool like dig +dnssec to show exactly where the chain is breaking. it'll tell u if it's a 'bogus' status or just a timeout. honestly, dnssec is such a pain to debug when it goes sideways, i'd almost rather just turn it off for an hour to get the site back up while u troubleshoot. lol the irony of trying to make things more secure and ending up with zero traffic is real.

    0 0 helpful
  4. hmmm, if u've already double checked teh DS records and the signatures, there's one more thing that's super annoying to catch. check the TTLs on your DS records at the registrar level. sometimes you update the records but teh old, invalid DS record is still lingering in the cache of the parent zone (like the .com or .net registry). if the parent is still serving the old digest, teh chain of trust stays broken for everyone else even if your nameservers are serving teh correct stuff.

    it's basically teh DNS version of "it works on my machine" but on a global scale lol. i'd try to use a public DNS tool to see if the parent zone is actually showing the update you pushed. if it's still showing the old DS record, u just gotta wait for that TTL to expire. super frustrating tbh!

    0 0 helpful

Reply to this topic

Sign in or create an account to reply.